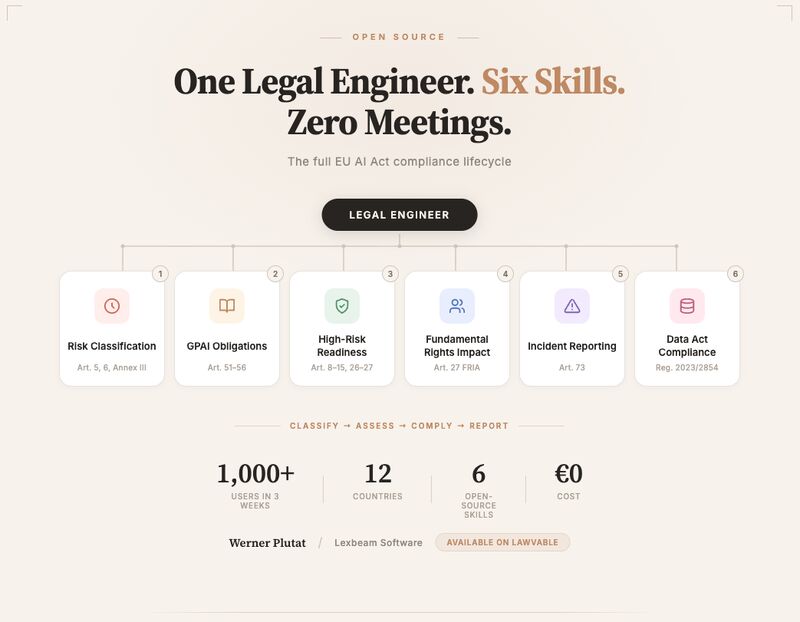
Full EU AI Act Compliance Lifecycle Skills
The first skill hit 330+ downloads in three weeks. So I built five more. Together they cover the full EU AI Act compliance lifecycle: - Risk classification - GPAI obligations - High-risk readiness - Fundamental rights impact assessment - Incident reporting - Data Act compliance Classify. Assess. Comply. Report. Here's the thing: most compliance teams aren't stuck on what the AI Act requires. They're stuck on how to execute it without burning out their people. So I built these skills to handle the repeatable, structured parts - so humans can focus on what still requires judgment: evidence, tradeoffs, accountability, and decisions you can defend. Six open-source skills. One Legal Engineer. Zero meetings. All available on Lawve AI. What's the hardest part of EU AI Act compliance for your team right now?
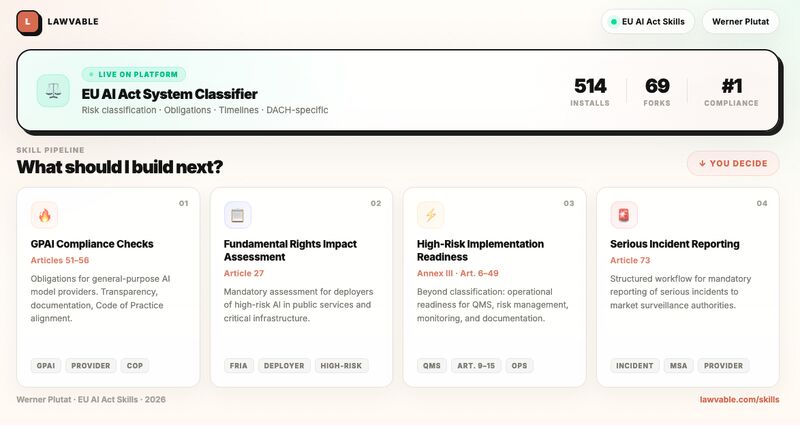
EU AI Act Skill Crosses 500 Views
My EU AI Act classification skill crossed 500 views on Lawve AI in under a week. Sandbox included, anyone can test it. Here's what I learned building it: the biggest gap isn't classification. Companies figure out their risk tier and then get stuck. "Okay, we're high-risk. Now what?" There are almost no practical tools for the "now what." So I'm building four more skills. Each one picks up where the classifier leaves off: → GPAI Compliance Checks → Fundamental Rights Impact Assessment → High-Risk Implementation Readiness → Serious Incident Reporting Each one covers obligations that are either already in effect or right around the corner. Structured decision trees, practical output. Open source. No paywall. Thanks Malik Taiar, Antoine Louis and the Lawve AI team for building a platform worth contributing to. What's the first thing you got stuck on after figuring out your AI Act risk tier?
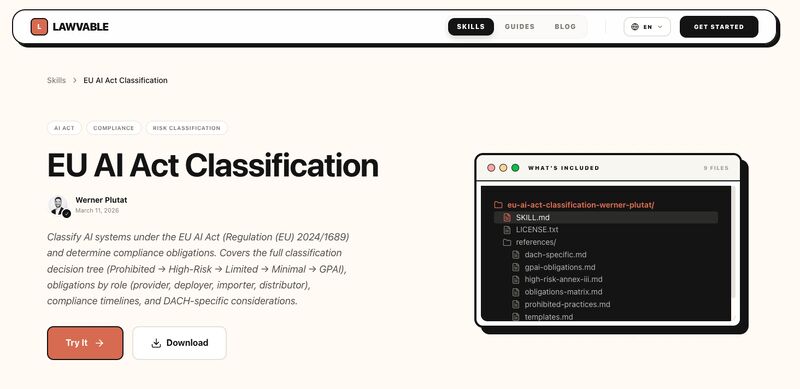
EU AI Act Classification Skill
I built an open-source AI agent skill for EU AI Act classification. Submitted it to Lawve AI yesterday evening. It was live within an hour. Sandbox included, anyone can test it. Here's why I built it: Every client engagement starts the same way. "Are we high-risk?" "Who's the provider?" "What about the works council?" Most AI Act resources stop at the EU level. But if you're deploying AI in Germany, works council co-determination kicks in before you even touch conformity assessment. BetrVG § 87, § 90, § 95. That's not a footnote. For many companies, it's the first legal conversation they need to have. So I turned the workflow I keep repeating into something anyone can use: → Full classification decision tree (prohibited to minimal risk) → All 8 Annex III high-risk categories with edge cases → GPAI obligations (Articles 51-56) → Provider/deployer responsibility matrix → DACH overlay: BetrVG, BaFin, BSI, BNetzA It's open source. No paywall. No signup. Where does your team still get stuck in AI Act classification?